So far this month we’ve covered the inbox, your team, and your passwords. Each of those layers stops a huge share of attacks. But a determined attacker only needs one opening, and eventually, something gets through.
When that happens, the question is simple: will you notice in minutes, or in weeks?
That answer depends on what’s watching your computers and servers, the devices security professionals call endpoints. For many businesses, that’s still traditional antivirus. In this post, we’ll explain why that’s no longer enough and what endpoint detection and response (EDR) does differently.
What does traditional antivirus do?
Traditional antivirus scans files and compares them to a database of known threats, called signatures. If a file matches something on the list, antivirus blocks or removes it.
That approach works well against older, widely circulated malware. It’s fast, lightweight, and still useful as a baseline. The problem is that it only recognizes what it has seen before. A brand-new piece of malware, or a slightly modified version of an old one, may not match anything in the database.
Why isn’t antivirus enough to protect a business today?
Antivirus isn’t enough because many modern attacks don’t rely on known malware files. Attackers increasingly log in with stolen credentials and use legitimate tools already on your systems, so there’s nothing for a signature scan to catch.
Security professionals call this “living off the land.” An attacker might:
- Sign in with a stolen password, so the login looks valid
- Use built-in Windows tools like PowerShell to run commands
- Install a legitimate remote access program to come back later
- Quietly disable backups and security settings before launching ransomware
Every one of those steps uses software that’s supposed to be there. To signature-based antivirus, it all looks normal. Attackers know this, which is why they’ve shifted their methods.
What is endpoint detection and response (EDR)?
Endpoint detection and response (EDR) is security software that continuously monitors activity on computers and servers, looks for suspicious behavior, and can respond automatically to stop a threat. Instead of asking “is this file known to be bad?”, EDR asks “is this behavior normal?”
EDR looks at patterns like:
- A program trying to encrypt large numbers of files quickly
- An account running admin commands it has never used before
- New persistence mechanisms that let software survive a reboot
- Security tools being disabled or tampered with
- Connections to known malicious infrastructure
When something suspicious happens, EDR records exactly what occurred, step by step. That record shows where an attack started, what it touched, and whether it spread.
How does EDR stop ransomware?
EDR stops ransomware by recognizing the behavior that comes before and during encryption, then cutting the attack off. It can kill the malicious process, isolate the infected device from the network, and in many cases roll back changes made to files.
Isolation is especially important. An infected laptop that’s disconnected from the network can’t spread ransomware to your file server. EDR can do that automatically, in seconds, while still letting your IT team connect to the device to investigate.
The difference between catching ransomware on one laptop and finding it across your entire network on Monday morning is often the difference between a minor inconvenience and a business-stopping event.
Ransomware attackers now spend about 20 hours inside before striking
Average time from break-in to ransomware rose from 17 to 20 hours, a window for a 27/7 SOC to catch them.
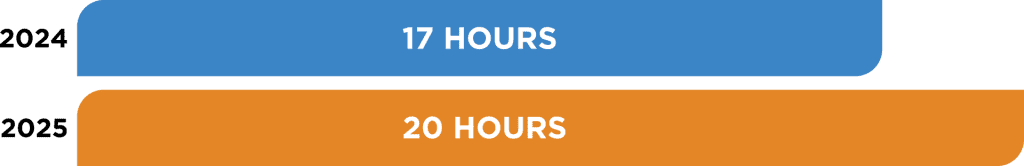
Average time-to-ransom, as reported in the Huntress 2026 Cyber Threat Report.
Huntress 2026 Cyber Threat Report · average time-to-ransom
Attackers increasingly move low and slow, stealing data before they encrypt anything. That quiet window is where behavior-based EDR and a 24/7 SOC earn their keep, especially when it falls on a night or weekend. Source: Huntress 2026 Cyber Threat Report.
Why does EDR need people behind it?
EDR produces alerts, and alerts only protect you if someone reviews them and acts quickly. A tool that flags suspicious activity at 2 a.m. on a Saturday doesn’t help if nobody sees it until Monday.
That’s why we deliver EDR as a managed service. The endpoint protection we deploy for clients is backed by a 24/7 security operations center (SOC): security analysts who monitor around the clock, investigate suspicious activity, separate real threats from false alarms, and respond when something needs action, including nights, weekends, and holidays. Your team isn’t left sorting through technical alerts it doesn’t have time or training to interpret.
For a small or mid-sized business, managed EDR offers protection that used to be available only to companies with their own security departments.
What is a 24/7 SOC?
A 24/7 security operations center (SOC) is a team of security analysts who monitor alerts and respond to threats around the clock, every day of the year. A managed SOC gives a small business that coverage without hiring and staffing its own security team.
Attackers often strike on nights, weekends, and holidays because they expect fewer people to be watching. A 24/7 SOC takes that advantage away.
Does EDR replace antivirus?
EDR generally includes or works alongside antivirus-style protection, so it builds on what antivirus does rather than throwing it away. Known threats still get blocked instantly. EDR adds behavior monitoring, investigation, and response on top.
Think of antivirus as a lock on the door and EDR as a monitored security system with cameras. The lock still matters. But if someone gets in anyway, you want to know immediately, see where they went, and stop them.
What should you ask about the protection on your devices?
If you’re not sure what’s protecting your computers and servers, start with a few questions:
- Is every device covered, including laptops that leave the office?
- Does our protection look for suspicious behavior, or only known malware?
- Who reviews alerts, and how quickly?
- Can an infected device be isolated automatically?
- Would we know if an attacker logged in with a valid password and started poking around?
If any of those answers is “I don’t know,” that’s worth a conversation.
Let’s find out what’s watching your devices
At Absolute, we do IT differently. We work as an extension of your team, and that includes keeping watch when you’re not. If you want to know whether your current protection would catch a modern attack, we’ll give you a straight answer.
Call us at 903-807-0303 or reach out via our contact form.
Share this Post