TL;DR: Shadow IT occurs when employees use unauthorized software, applications, cloud services, or devices without IT approval. While often well-intentioned, these tools can introduce security risks, compliance challenges, and unnecessary costs. Organizations can reduce shadow IT by improving visibility, streamlining technology requests, and strengthening collaboration between IT and business teams.
Every organization has experienced it.
An employee uploads company files to a personal cloud storage account to collaborate faster. A department adopts a new project management platform because the approved solution feels outdated. A developer launches a cloud environment without involving IT.
These decisions may seem harmless in isolation, but together they contribute to one of the most significant challenges facing modern IT departments: shadow IT.
As organizations embrace cloud computing, remote work, and digital transformation, employees have more technology choices than ever before. Understanding why shadow IT happens and how to manage it effectively is essential for maintaining security while enabling productivity.
What Is Shadow IT?
Shadow IT refers to any technology used within an organization without the knowledge, approval, or oversight of the IT department. This includes software applications, cloud services, hardware devices, and online tools that employees adopt on their own.
Shadow IT exists because modern technology is easy to access. Employees can subscribe to a SaaS application, create a cloud account, or download productivity software in minutes without involving IT.
Common examples of shadow IT include:
- Cloud Storage Platforms: Employees storing company files in personal Dropbox, Google Drive, or OneDrive accounts.
- Collaboration Tools: Teams using Slack, WhatsApp, or other messaging platforms outside approved communication channels.
- Business Applications: Marketing, finance, or HR departments purchasing specialized software independently.
- Cloud Infrastructure: Developers provisioning servers or environments through public cloud providers without IT oversight.
- Personal Devices: Employees accessing corporate data from unmanaged laptops, tablets, or smartphones.
While these tools often improve efficiency, they also create challenges for security, governance, and operational management.
Why Shadow IT Continues to Grow
Shadow IT isn’t a new phenomenon, but it has expanded rapidly with the growth of cloud-based services and self-service technology platforms.
Today, employees can deploy tools on demand, frequently without purchasing hardware or waiting for IT support. This convenience accelerates innovation but also creates blind spots for organizations attempting to maintain security and compliance.
The reality is simple: employees usually adopt shadow IT because they believe it helps them work faster and more effectively.
The Risks of Shadow IT
Not every unauthorized application creates immediate problems. However, without proper oversight, shadow IT can expose organizations to significant risks.
Increased Security Vulnerabilities
Applications that have not undergone security reviews may lack important safeguards such as encryption, multi-factor authentication, access controls, or secure data storage practices.
These weaknesses can increase the likelihood of:
- Data breaches
- Unauthorized access
- Credential theft
- Malware infections
- Accidental data exposure
When IT is unaware of a tool’s existence, it cannot properly secure or monitor it.
Compliance and Regulatory Challenges
Organizations operating within regulated industries must maintain strict control over how sensitive information is stored, transmitted, and accessed.
When employees use unapproved applications, data may be stored in locations that violate internal policies or regulatory requirements, potentially creating compliance concerns.
Industries commonly affected include:
- Healthcare
- Financial services
- Legal services
- Government contractors
- Education
Without visibility into where data resides, organizations may struggle to demonstrate compliance during audits or investigations.
Unnecessary Technology Spending
Shadow IT often leads to duplicated purchases across departments.
For example, multiple teams may independently subscribe to similar project management, communication, or analytics platforms without realizing the organization already pays for an approved solution. 
The result is:
- Redundant software subscriptions
- Higher licensing costs
- Inefficient resource allocation
- Increased support complexity
Over time, these hidden expenses can become substantial.
Reduced Visibility and Control
Perhaps the greatest challenge shadow IT creates is reduced visibility.
IT teams cannot secure, monitor, govern, or support technology they do not know exists. As the number of unauthorized tools grows, organizations develop technology blind spots that make risk management increasingly difficult.
Why Employees Turn to Shadow IT
Addressing shadow IT requires understanding employee motivations rather than simply enforcing stricter rules.
Employees Need Results Quickly
Business priorities move fast. If software approval processes take weeks or months, teams often seek alternative solutions to meet deadlines.
Consumer Technology Sets High Expectations
Today’s workforce is accustomed to intuitive, user-friendly applications. Employees naturally gravitate toward tools that help them work more efficiently.
IT Is Sometimes Viewed as a Bottleneck
When users assume every request will be rejected or delayed, they are more likely to bypass official processes altogether.
Lack of Awareness
In many cases, employees don’t fully understand which tools are approved, what the risks are, or why approval matters.
This means shadow IT is frequently a communication issue as much as a technology issue.
Best Practices for Managing Shadow IT
The goal is not to eliminate shadow IT completely. Instead, organizations should focus on improving visibility, reducing risk, and making it easier for employees to adopt approved solutions.
Build Stronger Partnerships Across Departments
IT should engage with business units regularly to understand operational challenges and upcoming technology needs.
Collaborative planning helps identify requirements before employees seek alternatives on their own.
Educate Employees
Effective security awareness programs should explain:
- What shadow IT is
- Why it creates business risk
- How employees can request new technology
- Which tools are approved for use
Education creates alignment and helps employees make informed decisions.
Improve the User Experience
If users consistently look elsewhere for solutions, it may indicate that approved tools are not meeting business needs.
Organizations should evaluate whether existing platforms remain competitive, useful, and easy to use.
Invest in Visibility Tools
You can’t manage what you can’t see.
Technologies such as:
- Cloud Access Security Brokers (CASBs)
- SaaS management platforms
- Network monitoring solutions
- Endpoint management tools
can help organizations identify unauthorized applications and understand how they are being used.
Establish Clear Policies
Technology policies should clearly outline:
- Approved technology standards
- Data handling requirements
- Procurement procedures
- Approval workflows
- Employee responsibilities
Clear expectations reduce ambiguity and encourage compliance.
The Modern Role of IT
The most successful organizations no longer position IT as a gatekeeper.
Instead, modern IT departments act as strategic partners that balance security with business agility. Their role is to enable innovation while managing risk, not simply approve or deny requests.
This approach often includes:
- Faster approval workflows
- Self-service options for low-risk tools
- Department-specific technology planning
- Ongoing communication with business leaders
When employees trust IT to help solve problems, they are less likely to seek solutions outside approved channels.
Creating a Proactive Shadow IT Strategy
Shadow IT is often a symptom of a larger issue: employees are trying to solve business problems faster than existing processes allow.
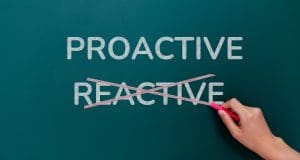
Organizations that treat shadow IT solely as a policy violation risk driving the behavior underground. Organizations that view it as valuable feedback gain insight into unmet business needs and opportunities for improvement.
A proactive strategy begins with visibility. Identify which tools employees are using, understand why they chose them, assess the associated risks, and determine whether those tools should be approved, replaced, or retired.
Shadow IT will never disappear entirely. However, with the right combination of governance, technology, communication, and collaboration, organizations can significantly reduce risk while empowering employees to work effectively.
Frequently Asked Questions
- What is the difference between shadow IT and rogue IT?
- Shadow IT usually involves employees using technology without approval but without malicious intent. Rogue IT generally describes deliberate violations of IT policies and may involve knowingly bypassing controls or governance requirements.
- How common is shadow IT?
- Extremely common. Most organizations have some form of shadow IT, particularly as cloud-based applications become easier to access and deploy.
- What tools help identify shadow IT?
- Organizations commonly use CASBs, SaaS management platforms, endpoint management solutions, and network monitoring tools to discover unauthorized applications and services.
- Is shadow IT always a security risk?
- Not necessarily. However, any technology that has not been assessed for security, compliance, and operational requirements typically introduces additional risk compared to approved solutions.
- What should IT do when shadow IT is discovered?
- IT should first understand the business problem the tool was solving. From there, the organization can evaluate risk and determine whether to approve the tool, provide an alternative solution, or remove it altogether.
Works Cited
- Cloud Security Alliance. (2024). What is shadow IT? Retrieved from https://cloudsecurityalliance.org
- European Union. (2016). General Data Protection Regulation (GDPR). Retrieved from https://gdpr.eu
- Gartner. (2023). Top strategic predictions for IT organizations and users. Gartner Research.
- U.S. Department of Health & Human Services. (2024). Health Insurance Portability and Accountability Act (HIPAA) for professionals. Retrieved from https://www.hhs.gov/hipaa
- Microsoft. (2024). Defend against shadow IT with Microsoft Defender for Cloud Apps. Retrieved from https://learn.microsoft.com
- National Institute of Standards and Technology. (2024). Cybersecurity Framework (CSF) 2.0. Retrieved from https://www.nist.gov/cyberframework
- BetterCloud. (2024). State of SaaS operations report. Retrieved from https://www.bettercloud.com
- Torii. (2024). SaaS management and shadow IT visibility resources. Retrieved from https://www.toriihq.com
Share this Post